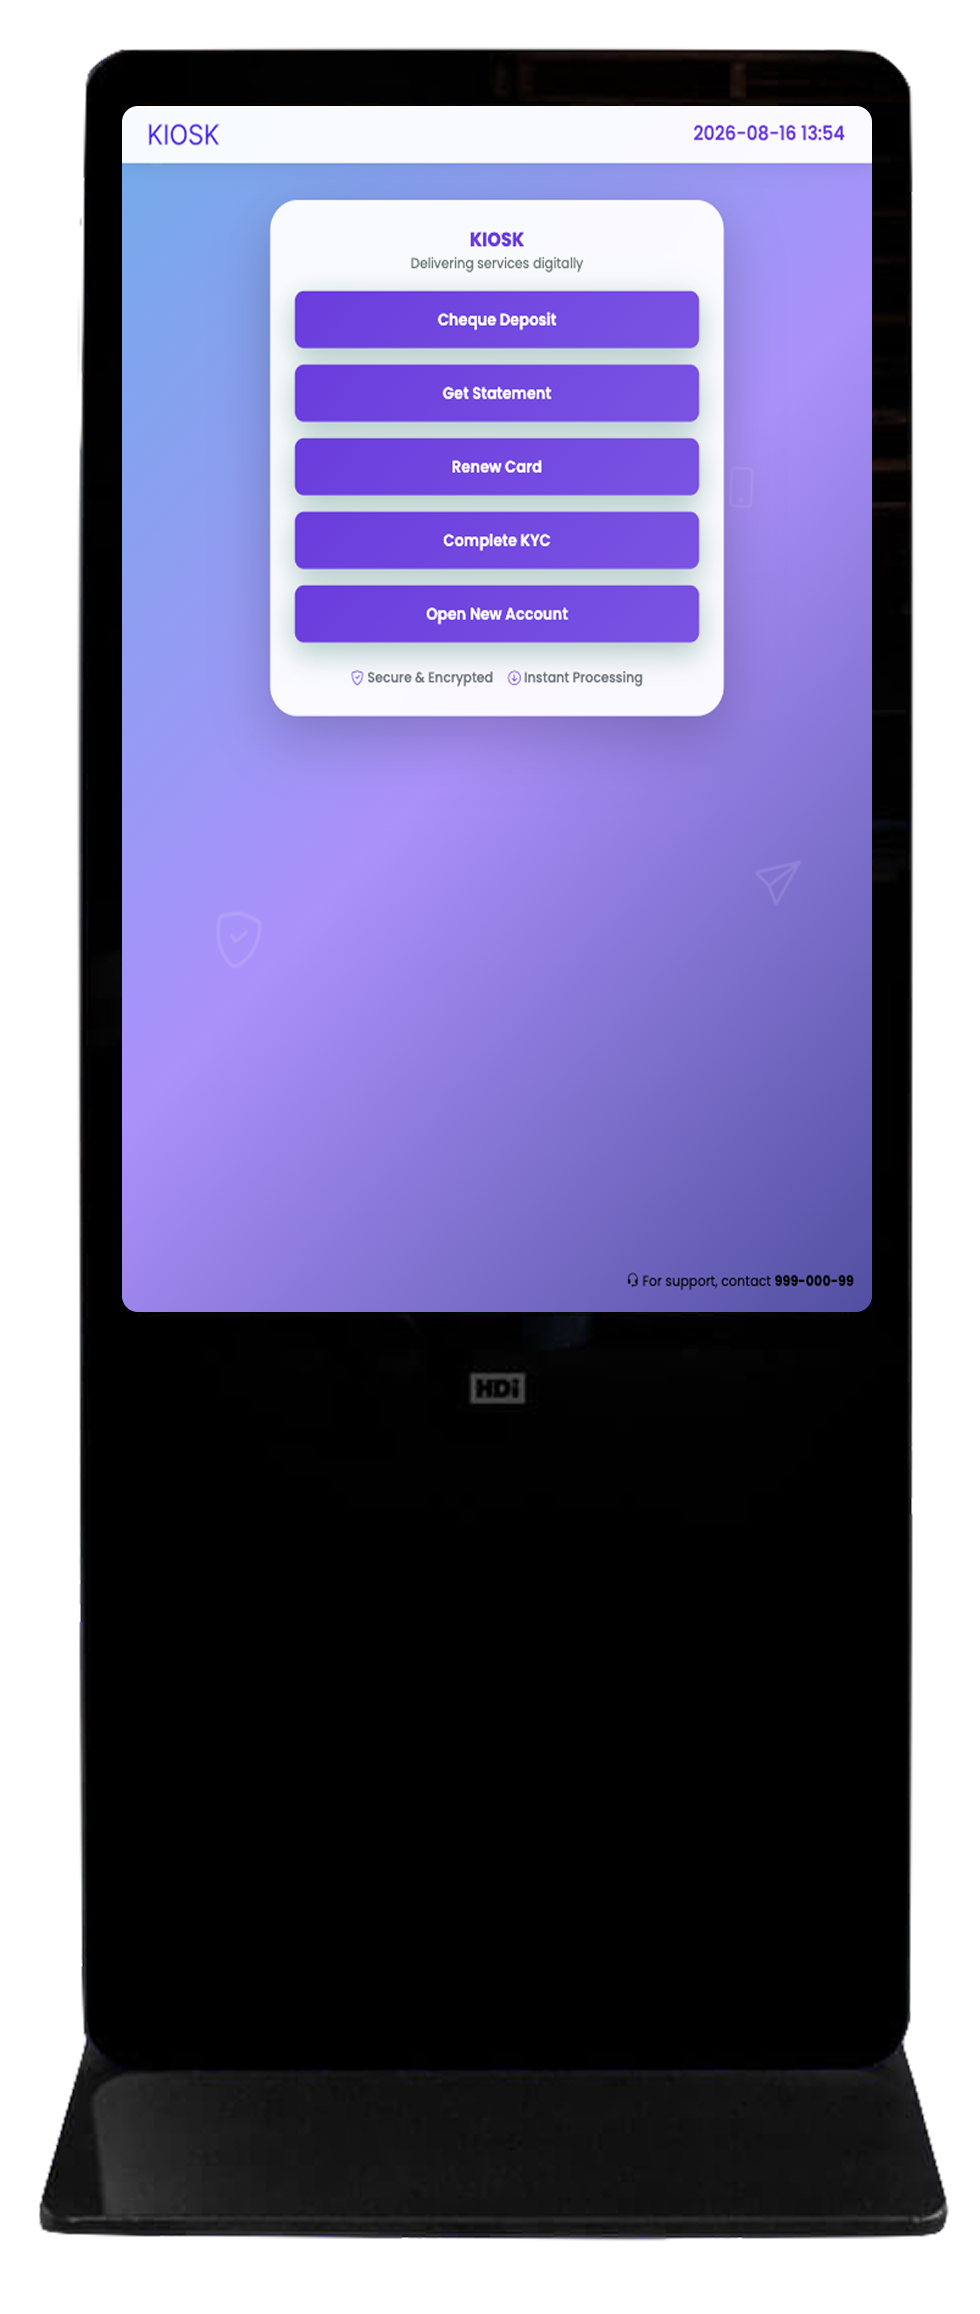
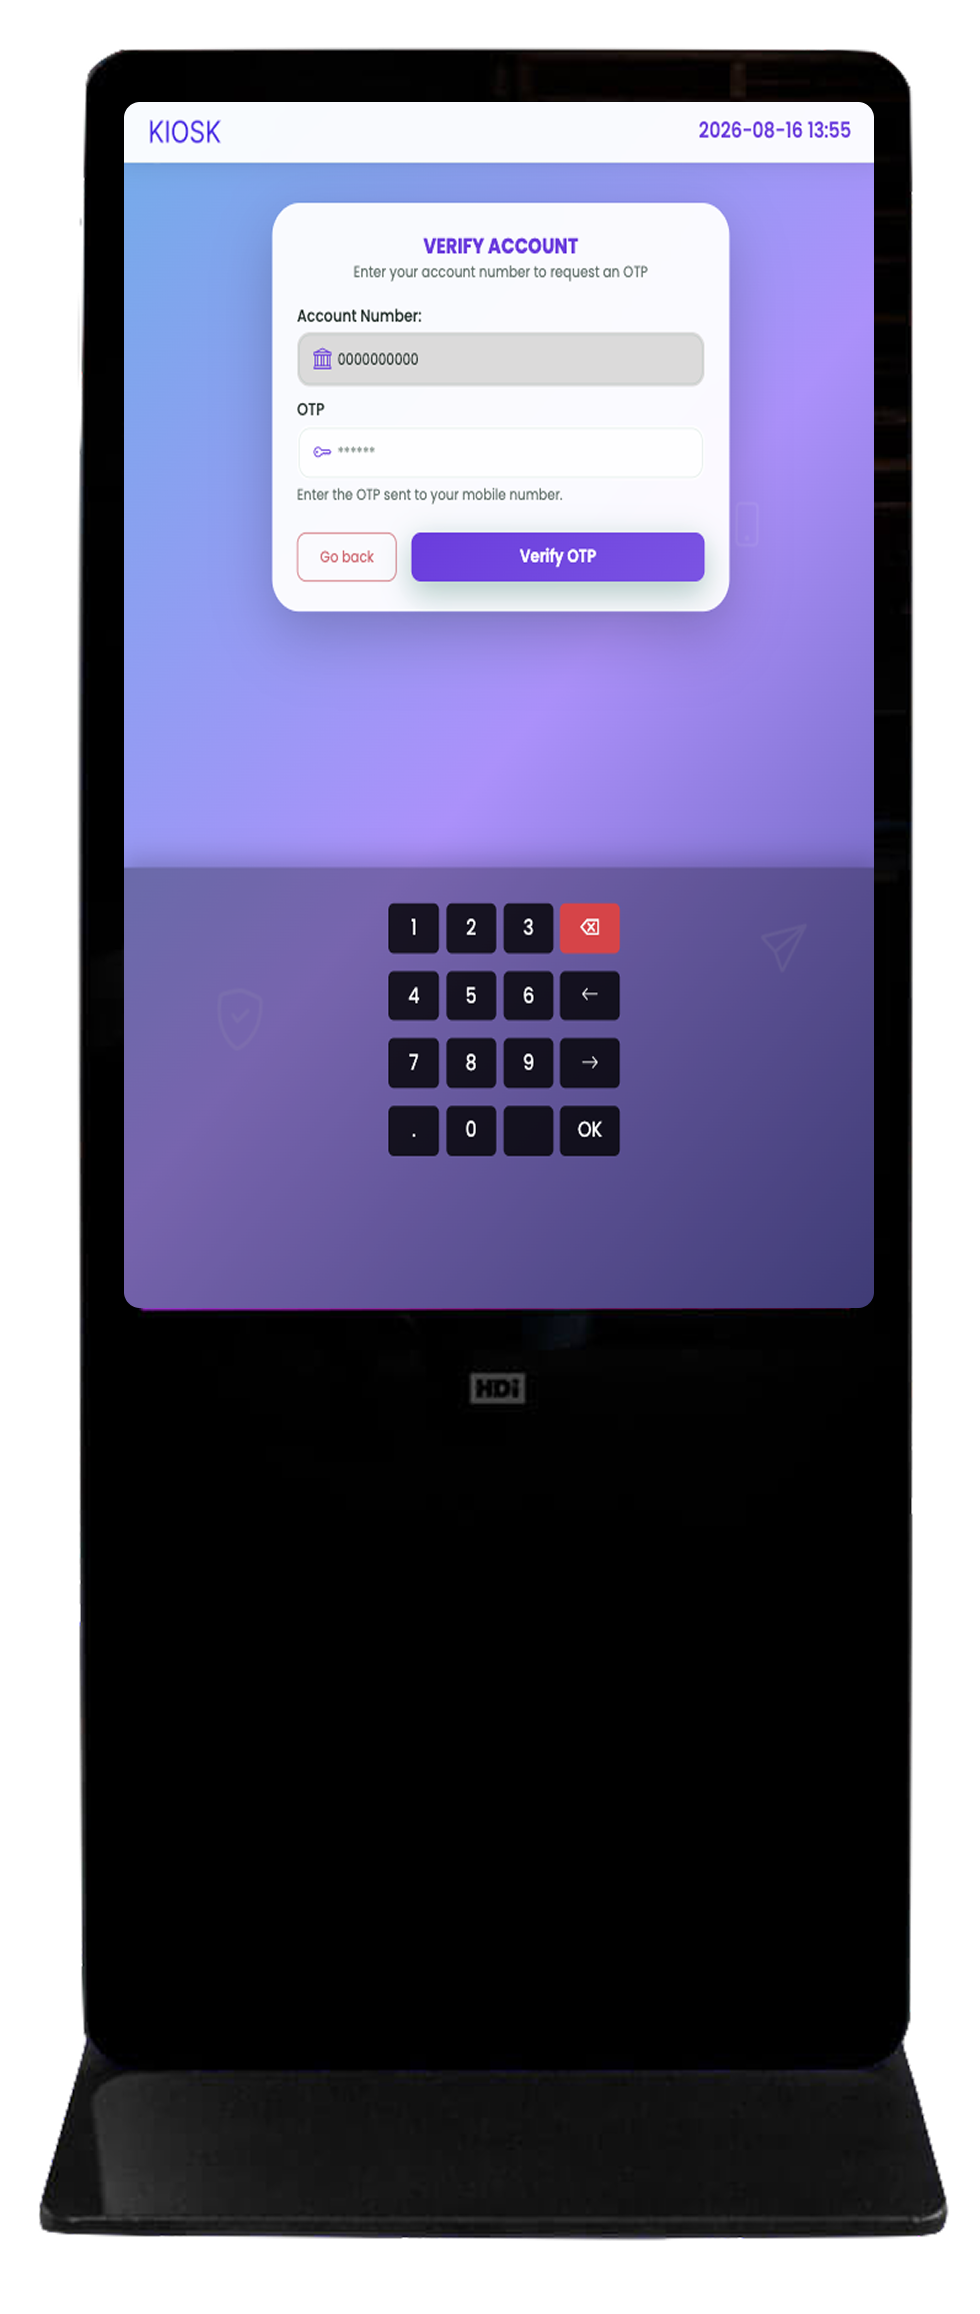
A self-service kiosk application built for a vendor providing kiosk banking services across roughly 40% of the country's coverage, designed to be secure enough for public deployment while supporting advanced features like AI-powered cheque deposit.
The system was built around a problem specific to public-facing financial infrastructure: a kiosk sitting in a public place is a physically exposed endpoint into a bank's systems, and it has to be secured, monitored, and made intelligent enough to handle real financial tasks — like reading a handwritten cheque — without a human present.
Kiosk banking exists to extend banking access into public spaces without the cost of a full branch — but that convenience comes with a security trade-off a branch doesn't have: the machine itself is physically exposed, unattended, and reachable by anyone.
For a vendor deploying kiosks across a large share of the country, that risk wasn't isolated to one machine — it was multiplied across every unit in the field.
At the same time, the value of a kiosk depends on how much it can actually do without a teller present. A kiosk that can only dispense cash isn't much more useful than an ATM.
Supporting something like cheque deposit — traditionally a task requiring a person to read and verify handwriting — meant the kiosk needed real intelligence built in, not just a scanner and a slot.
And because this was a platform serving multiple client banks rather than one institution, it also needed to be flexible enough that different clients could adopt different subsets of functionality instead of every deployment being a fixed, one-size-fits-all build.
The core challenge was building a platform that could be trusted with financial transactions in an unsecured physical environment, extend that trust down to individual field devices through certificate-based authentication, run AI-based cheque processing reliably, and remain configurable across different clients and deployments.
Every publicly deployed kiosk needed a strong device identity appropriate for unattended endpoints operating outside controlled environments.
Certificate management had to live at the application layer rather than depend entirely on proxy infrastructure, keeping trust decisions close to the system that actually used them.
The CX30 cheque scanner needed to be controlled by the trusted switch rather than allowing the physically exposed kiosk to make hardware decisions independently.
Handwritten cheque fields had to be extracted through AI and then validated carefully enough that uncertain output could never become an automatically trusted financial instruction.
The platform needed to preserve the same security and control model across a large fleet of geographically distributed machines.
Different banks needed to enable different feature sets on top of the same underlying platform without creating separate bespoke codebases.
In effect, the system needed to function less like a single kiosk application and more like a distributed, security-first platform — with intelligence and control concentrated at the switch, and the kiosk itself treated as an untrusted edge device until proven otherwise.
I was responsible for the architecture and development of the platform, with ownership spanning security, the cheque deposit AI pipeline, and the configurable feature architecture.
The key architectural responsibility was making sure that no matter how exposed a kiosk was physically, the platform's actual trust and intelligence lived in places that couldn't be tampered with in the field — the application layer and the switch, not the kiosk itself.
A kiosk deployed in a public space had to be treated as a potentially hostile endpoint until it proved its identity through certificate-based authentication. Even a compromised kiosk could not be allowed to exercise more authority than the backend had explicitly granted it.
Moving certificate configuration away from the proxy meant the application making the trust decision could manage that trust directly, making certificate behavior easier to control and audit.
Letting the kiosk control the cheque scanner directly would have increased the authority of an exposed device. Routing scanner control through the switch kept hardware actions behind a trusted backend decision.
The AI pipeline had to handle real handwriting while remaining conservative around uncertainty. The validation layer around TrOCR was therefore just as important as the recognition model itself.
Features such as cheque deposit needed to remain modular rather than become hard-coded into one implementation, allowing different client banks to adopt the capabilities relevant to them without fragmenting the platform into separate codebases.
This project changed how I think about designing systems for physically exposed environments. It's tempting to design a kiosk as if it were simply another client application talking to a backend.
In reality, a publicly deployed kiosk needs to be treated as an adversarial environment by default — every design decision, from where certificates live to who controls the scanner, has to assume the device itself could be tampered with.
The AI side reinforced a related lesson: automating handwriting recognition isn't valuable on its own if the system blindly trusts the output. The real engineering work was pairing the AI pipeline with validation rigorous enough to justify trusting it with money.
I'm always open to conversations around interesting problems, ideas, and opportunities to work together.
Reach out at hi@riteshr.au